






Privacy Notice
Last updated: 7 October 2026
Virtual Headquarters Limited (VHQ) values your privacy and respects the rights you have in relation to your personal data. This Privacy Notice (Notice) lets you know how we use your personal data and provides details of your rights under data protection law.
It is important that you read this Notice together with any other privacy notice(s) we may provide so that you are fully aware of how and why we are using your personal data. This notice supplements all other privacy notices provided by us and is not intended to override them.
Who does this notice relate to?
- This Notice gives you information about how we collect and use your personal data when:
- you are our customer when you buy a product or service from us (Customer)
- you are a prospective customer, (Prospective Customer);
- you provide goods or services to us and we need to process your personal data in order to enter into an agreement or contract with you and manage that agreement or contract; (Supplier) and
- you use this website https://www.virtual-headquarters.com/.
- Our services and our website are not intended for children and we do not knowingly collect personal data relating to children.
Who is the controller of your personal data?
- Virtual Headquarters Limited (registered number 09556484) is the controller for your personal data (referred to as “VHQ”, “we”, “us” or “our” in this notice). VHQ is registered with the Information Commissioner’s Office (ICO) with registration number ZA179926.
What happens if this Notice is updated or your personal data changes?
- This Notice was last updated on the date stated at the beginning of the Notice and any historic versions can be obtained by contacting us at [email protected]. We will publish any changes to this Notice on our website. It is important that the personal data we hold about you is accurate and up to date. Please keep us informed if your personal data changes during your relationship with us.
Definitions
- Please find below some key definitions which are used when describing types of personal data:
| Key term | Definition |
|---|---|
| personal data | any information about an individual who is identified or identifiable |
| special categories of personal data | any information about you which relates to your race or ethnicity, religious or philosophical beliefs, sex life, sexual orientation, political opinions, trade union membership, your health as well as genetic data and biometric data for the purpose of uniquely identifying you. |
| criminal offence data | any personal data relating to criminal convictions and offences or related security measures. |
- We may be required to collect criminal offence data, for example when we undertake anti-money laundering, anti-terrorism checks, or background checks, however, we will tell you if this is the case at the time of collection.
What personal data do we collect about you?
- We collect, use, store and transfer different kinds of personal data about you which we have grouped together in the table below. The terms below are mainly used in Section 8 (What do you use my personal data for and why?) to explain why we use the personal data in the way we do:
| Description | Personal data |
|---|---|
| Communication Data | The channel and method by which we communicate with you, the contents of communications with you, including emails, correspondence and, where applicable, telephone call recordings. |
| Contact Data | Correspondence addresses, personal and professional email addresses, details of the company you work for, contact information in social media profiles, personal and professional telephone numbers and business cards |
| Financial Data | bank account details, billing information, transaction and payment card information |
| Identity Data | Full name, title, date of birth, gender, residential address, email address, copies of government-issued identification documents (including passports and driving licences), a live “selfie” image of your face which is used to create a biometric template for the purpose of facial matching with your identity document, SmartSearch verification results. |
| Marketing Data | your preferences in receiving marketing from us |
| Transaction Data | details about payments to and from you and other details of services we have provided to you and details of services you provide to us where you are a supplier or provider of goods and services |
| Technical Data | internet protocol (IP) address, browser type and version, time zone setting, location, browser plug-in types and versions and operating system and platform |
| Usage Data | information about how you use our website and services |
| Call Recording Data | Audio recordings of telephone calls, together with any information discussed during the call and associated metadata, such as the date, time and telephone number. |
What happens if you don’t provide us with your personal data?
- Where we need to collect personal data because:
- we are complying with a legal or regulatory obligation or
- we need it under the terms of a contract we have with you, or
- the information is necessary to enter into a contract with you
- and you fail to provide that personal data when requested, we may not be able to perform the contract we have or are trying to enter into with you. In this case, we may have to decline to provide goods or services to you or enter into a contract with you, but we will notify you if this is the case at the time.
How do we collect personal data about you?
- We collect personal data from and about you using the following methods:
| Collection method | Description |
|---|---|
| Direct interactions | Most of the personal data we collect and use comes directly from you in person, by telephone or via email |
| Automated technologies or interactions | As you interact with our website, we automatically collect Technical data. We collect this personal data by using cookies, server logs and other similar technologies. You can see a copy of our cookie notice by clicking on the cookie banner on our website. |
| Third parties | We receive personal data about you from the third parties listed below: a) SmartSearch – identity verification information and electronic identity verification results as part of the customer due diligence process. b) Professional advisers and authorised representatives – including accountants, solicitors or other representatives authorised to act on your behalf, where they provide information in connection with our services. c) Regulatory, law enforcement and government bodies – where personal data is provided to us to enable us to comply with our legal and regulatory obligations. |
| Via our IT systems | We automatically collect certain technical information when you use our website or online services. This may include your IP address, browser type and version, device information, operating system, usage data, cookies and similar technologies. |
| Publicly available sources | We may receive personal data from publicly available sources where this is necessary to carry out customer due diligence, comply with our legal and regulatory obligations or undertake ongoing monitoring. These sources include Companies House, sanctions lists, Politically Exposed Person (PEP) registers, insolvency registers, publicly available adverse media and publicly accessible social media information used as part of customer due diligence and ongoing monitoring. |
What do we use your personal data for and why?
- We will only use your personal data where the law allows us to. Most commonly, we will use your personal data in the following circumstances:
- To comply with a legal or regulatory obligation, including our obligations under the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017, the Companies Act 2006, applicable tax legislation and other legal or regulatory requirements.
- Where it is in our legitimate interests, or those of a third party, provided your interests and fundamental rights do not override those interests. This includes managing and administering our business, providing and improving our services, maintaining the security of our systems, preventing fraud, responding to enquiries, recovering debts and protecting our legal rights. We will always consider and balance any potential impact on your rights and freedoms before we process your personal data for our/ a third party’s legitimate interest.
- Performance of a contract to which you are a party or to take steps at your request before entering into such a contract; and
- Where you have given your consent, where consent is required. For example, we may rely on your consent to send you marketing communications. You can withdraw your consent at any time by clicking the unsubscribe link in our marketing emails or by contacting us at [email protected].
- for the purposes of a recognised legitimate interest such as sharing information with law enforcement authorities when it is necessary to prevent, detect or investigate crimes.
- to establish, exercise and/or defend any legal claims that may be brought by or against us.
- The table below explains the ways in which we use your personal data and the legal basis which is used.
| Individual | Purpose for processing | Data used | Legal basis relied on |
|---|---|---|---|
| Prospective Customers | To respond to enquiries received by telephone, email, our website or other communication channels and provide information about our services. | Identity Data, Contact Data, Communication Data, Call Recording Data | Legitimate interests – to respond to enquiries, provide information about our services and promote our business. |
| Prospective Customers | To assess whether our services are suitable for your requirements and provide quotations or proposals where requested. | Identity Data, Contact Data, Communication Data | Legitimate interests – to assess enquiries and provide information about our services before a contract is entered into. |
| Prospective Customers | To create customer records and progress the onboarding process before entering into a contract. | Identity Data, Contact Data, Communication Data | Performance of a contract – to take steps at your request before entering into a contract (Article 6(1)(b) UK GDPR). |
| Prospective Customers and Customers | To verify the identity of directors, Persons with Significant Control (PSCs) and Authorised Account Persons (AAPs) during customer onboarding using our identity verification provider. | Identity Data, Contact Data, Communication Data | Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. Explicit consent to process biometric data for the purpose of identification verification through facial matching during the customer onboarding process |
| Prospective Customers and Customers | To carry out Customer Due Diligence (CDD), verify customer identity, assess customer risk and determine whether a business relationship can be established or continued. | Identity Data, Contact Data, Communication Data | Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. |
| Prospective Customers and Customers | To carry out sanctions screening before establishing, and where appropriate during, the business relationship. | Identity Data, Contact Data | Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. |
| Prospective Customers and Customers | To identify whether customers or associated individuals are Politically Exposed Persons (PEPs), their family members or known close associates and determine the appropriate level of customer due diligence. | Identity Data, Contact Data | Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. |
| Prospective Customers and Customers | To undertake adverse media screening as part of our risk-based customer due diligence procedures. | Identity Data, Contact Data | Legitimate interests – to identify and assess potential financial crime, reputational and customer risk as part of VHQ’s risk-based customer due diligence procedures. |
| Prospective Customers and Customers | To communicate with customers throughout the onboarding process, request additional information where required and notify customers of the outcome of their application. | Identity Data, Contact Data, Communication Data | Performance of a contract – to take steps at your request before entering into a contract and administer the onboarding process. |
| Customers and individuals who have opted in to marketing | To send marketing communications about our services, updates and promotional offers where permitted by law. | Marketing Data, Identity Data, Contact Data, Communication Data, Technical Data, Usage Data | Legitimate interests to send marketing communications about our services to existing customers in relation to similar services, where they have not opted out of receiving such communications. Consent where the requirements for relying on our legitimate interests are not met. Individuals may withdraw their consent or unsubscribe from marketing communications at any time. |
| Customers | To provide services in accordance with the customer’s instructions and the agreed contract. | Identity Data, Contact Data, Communication Data, Transaction Data | Performance of a contract – to provide the services requested by the customer and administer the contractual relationship. |
| Customers | To administer customer accounts, maintain customer records, manage authorised contacts, process account changes and communicate important information relating to the customer’s account and services. | Identity Data, Contact Data, Communication Data, Transaction Data | Performance of a contract – to administer the customer relationship and provide our services. |
| Customers | To verify the identity of customers and authorised contacts before making changes to customer accounts or services, including verifying their authority to request account changes. | Identity Data, Contact Data, Communication Data | Performance of a contract – to protect customer accounts, prevent unauthorised access and administer our services securely. |
| Customers | To process subscriptions, issue invoices, collect payments, administer refunds where applicable and maintain accounting records relating to the services provided. | Identity Data, Contact Data, Communication Data, Transaction Data | Performance of a contract – to administer our services and process payments. Legal obligation – to comply with applicable tax and accounting legislation. |
| Customers | To provide customer support, respond to service requests, investigate account queries and resolve issues relating to the services provided. | Identity Data, Contact Data, Communication Data, Transaction Data | Performance of a contract – to provide customer support and administer our services. |
| Customers | To manage customer cancellations, terminate services, calculate final charges and fulfil our legal and regulatory obligations following the end of the business relationship. | Identity Data, Contact Data, Communication Data, Transaction Data | Performance of a contract – to administer the termination of the contractual relationship. Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. |
| Customers | To disclose identity verification information to authorised London Building Partners where necessary to enable them to comply with their legal or regulatory obligations relating to occupiers using their premises. | Identity Data, Contact Data, Communication Data | Our legitimate interest in providing London Building Partners with the records they need to comply with the London Local Authorities Act 2007, so that VHQ can offer the virtual office service in these locations to customers. |
| Suppliers | To onboard suppliers, maintain supplier records, administer supplier accounts, manage contractual relationships, communicate with suppliers and process payments for goods and services provided to VHQ. | Identity Data, Contact Data, Financial Data, Transaction Data, Communication Data | Performance of a contract – to administer supplier relationships and fulfil our contractual obligations. |
| Customers | To carry out ongoing monitoring of customer relationships, including reviewing customer information, ownership structures and account activity where required throughout the business relationship. | Identity Data, Contact Data, Communication Data, Transaction Data | Legal obligation – to comply with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. |
| Customers, Prospective Customers and Suppliers | To prevent, detect and investigate fraud, financial crime, unauthorised use of our services and other unlawful activity. | Identity Data, Contact Data, Communication Data, Transaction Data, Technical Data, Usage Data | For our recognised legitimate interest to detect, investigate or prevent crime |
| Customers | To investigate, manage and respond to complaints, disputes and service issues. | Identity Data, Contact Data, Communication Data, Transaction Data | Legitimate interests – to investigate complaints, improve our services and protect our business. |
| Customers | To disclose personal data where required by law or in response to requests from regulators, law enforcement agencies, courts or other competent authorities. | Identity Data, Contact Data, Communication Data, Transaction Data | Legal obligation – to comply with applicable legal and regulatory obligations. |
| All individuals covered by this Privacy Notice | To establish, exercise or defend legal claims and protect the legal rights and interests of VHQ. | Identity Data, Contact Data, Communication Data, Financial Data, Transaction Data, Technical Data, Usage Data | Legitimate interests – to establish, exercise or defend legal claims and protect our business and legal rights. |
| All individuals covered by this Privacy Notice | To carry out internal audits, quality assurance reviews, compliance monitoring and respond to regulatory inspections or investigations. | Identity Data, Contact Data, Communication Data, Transaction Data | Legal obligation – to comply with applicable legal and regulatory obligations. Legitimate interests – to monitor compliance, improve our services and maintain effective business governance. |
| All individuals covered by this Privacy Notice | To administer, maintain and protect our IT systems, website, networks and business infrastructure, including monitoring system performance, troubleshooting, maintaining security and preventing unauthorised access. | Identity Data, Contact Data, Technical Data, Usage Data | Legitimate interests – to maintain the security, availability and integrity of our systems and services. |
| Website Users | To operate our website, analyse website usage, improve functionality and manage cookies and similar technologies. | Technical Data, Usage Data | Legitimate interests – to operate and improve our website. Consent – where required for non-essential cookies and similar technologies. |
| All individuals covered by this Privacy Notice | To maintain business records, produce management information, undertake business planning and ensure the effective administration of our business. | Identity Data, Contact Data, Communication Data, Transaction Data | Legitimate interests – to manage and develop our business effectively. |
| All individuals covered by this Privacy Notice | To comply with applicable legal, regulatory, accounting and tax obligations, maintain statutory records and demonstrate compliance with our legal responsibilities. | Identity Data, Contact Data, Communication Data, Financial Data, Transaction Data | Legal obligation – to comply with applicable legal and regulatory obligations, including company, tax and data protection legislation. |
- We will only use your personal data for the purposes for which we collected it, unless we consider that we need to use it for another reason and that reason is compatible with the original purpose. If you wish to obtain an explanation as to how the processing for the new purpose is compatible with the original purpose, please contact us at [email protected].
- If we need to use your personal data for an unrelated purpose, we will notify you and we will explain the legal basis which allows us to do so.
How do we use your personal data for marketing and how can you opt out?
- We may use your Identity Data, Contact Data, Communication Data, Technical Data and Usage Data to understand which of our services, updates and offers may be relevant to you.
You may receive marketing communications from us if you are an existing customer and we are permitted by law to send you marketing communications about similar services, provided you have not opted out of receiving them.
Where consent is required, you will only receive electronic marketing communications where you have actively opted in, for example by selecting the relevant marketing tick box on our website.
We do not currently send marketing communications to prospective customers unless they have specifically opted in to receive them.
- You can ask us to stop sending you marketing communications at any time by following the unsubscribe link included in our marketing emails or by contacting us at [email protected].
Where you opt out of receiving marketing communications, this will not prevent us from contacting you where necessary in connection with your account, the services we provide to you, or our legal or regulatory obligations.
What are your rights under data protection law?
- You have a number of rights in relation to how we use your personal data; these are set out below in more detail:
- Access – This enables you to receive a copy of the personal data we hold about you.
- Rectification – This enables you to have any incomplete or inaccurate personal data corrected.
- Erasure – This enables you to ask us to delete personal data where there is no good reason for us continuing to process it. Note, however, that we may not always be able to comply with your request for erasure because of specific legal reasons which will be notified to you, if applicable, at the time of your request.
- Objection – This enables you to object to the processing of your personal data where we are relying on our legitimate interest(s) (or that/those of a third party) and you object to processing on this ground as you feel the processing impacts your fundamental rights and freedoms. In some cases, we may demonstrate that we have compelling legitimate grounds to process your information which override your rights and freedoms. You also have the absolute right to object where we are processing your personal data for direct marketing purposes.
- Restriction – This enables you to ask us to suspend the processing of your personal data in the following scenarios: (a) where you want us to establish the accuracy of the personal data; (b) where our use of the personal data is unlawful but you do not want us to erase it; (c) where you need us to hold the personal data even if we no longer require it as you need it to establish, exercise or defend legal claims; or (d) where you have objected to our use of your personal data but we need to verify whether we have overriding legitimate grounds to use it.
- Portability – This enables you, in certain situations, to request transfer of your personal data to you or to a third party. We will provide your personal data (to you, or a third party you have chosen) in a structured, commonly used, machine-readable format.
- Your right to withdraw consent – If we are relying on consent to process your personal data, you can withdraw your consent at any time, however, this will not affect the lawfulness of any processing carried out before you withdraw your consent. If you do not wish to provide explicit consent to process your biometric data for the purpose of identification verification please contact [email protected] so that we can offer you a manual review as an alternative method of confirming your identity.
- If you wish to exercise any of the rights set out above, please contact us using the details set out in Section 2 (Who is the controller of my personal data?). If our legal basis for processing is consent and you wish to withdraw your consent, you can also use the methods set out in Section 8 (What do we use your personal data for and why?)
- Before we can process your request, we may need information from you to help us confirm your identity. This is a security measure to ensure that rights are being exercised by the correct person and to ensure that personal data is not disclosed to, erased by or altered by any person who has no right to do so.
- For more information on the rights set out above and when they apply, please contact us at [email protected] or see the guidance from the UK Information Commissioner on individuals’ rights.
Who do we share your personal data with and where do we transfer your personal data to?
- We may have to share your personal data with third parties for the purposes set out in the table in Section 8 (What do you use my personal data for and why?)
- Some of the third parties are based outside the UK and/or the European Economic Area (EEA) so their processing of your personal data will involve a transfer of personal data outside the UK and/or the EEA. Whenever we transfer your personal data out of the UK and/or the EEA, we ensure a similar degree of protection is afforded to it by ensuring at least one of the following safeguards is in place:
- We may transfer your personal data to countries that have been granted an adequacy decision by the European Commission and/or an adequacy regulation by the UK Secretary of State (as applicable) confirming that the country in question provides an adequate level of protection for personal data; or
- We may use specific contracts approved by the European Commission and/or the UK (as applicable) which ensure that personal data is adequately protected. When we rely on this measure, we will conduct risk assessments and take appropriate measures to ensure that the third-party can comply with the provisions of such contracts and we have confirmed that the country to which the personal data is transferred provides enforceable data subject rights and effective legal remedies for data subjects are available there; or
- a specific exception applies under applicable data protection law.
- Please see below for details of the third parties we share your personal data with and where we send your personal data:
- Service providers who provide IT and systems administration services and access to platforms we use for operational purposes to run our business;
| Third party | Personal data shared | Reason for sharing personal data | Is your personal data sent outside of the UK/EEA? |
|---|---|---|---|
| Microsoft 365 (Microsoft Ireland Operations Limited) | Identity Data, Contact Data, Communication Data, Technical Data, Usage Data and customer records. | To provide email, document management, cloud storage and business IT infrastructure. | Yes – Microsoft may process personal data outside the UK. Appropriate safeguards, including the UK International Data Transfer Addendum and/or Standard Contractual Clauses (SCCs), are in place where required. |
| Google Workspace (legacy systems only, where applicable) | Identity Data, Contact Data, Communication Data and historical customer records. | To retain historical business records held in legacy systems. | Yes – Google may process personal data outside the UK/EEA. Appropriate safeguards, including the UK International Data Transfer Addendum and/or Standard Contractual Clauses (SCCs), are in place where required. |
| BZB IT Solutions | Identity Data, Contact Data, Communication Data, Technical Data and customer records where access is required. | To provide IT support, system administration and maintenance. | No. |
| Pipedrive | Identity Data, Contact Data, Communication Data, Marketing Data and customer account information. | To manage customer relationships, sales opportunities and customer accounts. | No. |
| Chargebee | Identity Data, Contact Data, Financial Data, Transaction Data and Communication Data. | To manage subscriptions, billing and payment processing. | Yes – Chargebee may process personal data outside the UK/EEA. Appropriate safeguards, including the UK International Data Transfer Addendum and/or Standard Contractual Clauses (SCCs), are in place where required. |
| Xero | Identity Data, Contact Data and Transaction Data. | To maintain accounting records and prepare financial reports. | Yes – Xero may process personal data outside the UK/EEA. Appropriate safeguards, including the UK International Data Transfer Addendum and/or Standard Contractual Clauses (SCCs), are in place where required. |
- HM Revenue & Customs, regulators and other authorities based in the UK who require reporting of processing activities in certain circumstances, for example to ensure we are complying with legal and regulatory obligations;
| Third party | Personal data shared | Reason for sharing personal data | Is your personal data sent outside of the UK/EEA? |
|---|---|---|---|
| HM Revenue & Customs (HMRC) | Identity Data, Contact Data, Transaction Data and accounting records where required. | To comply with our legal and tax obligations. | No. |
| Information Commissioner’s Office (ICO) | Identity Data, Contact Data, Communication Data and other information relevant to the matter. | To comply with our obligations under data protection legislation. | No. |
| Other regulators and competent authorities | Identity Data, Contact Data, Communication Data, Transaction Data and other information required by law. | To comply with legal and regulatory obligations. | No. |
- Identity verification and customer due diligence providers used to comply with our anti-money laundering and legal obligations.
| Third party | Personal data shared | Reason for sharing personal data | Is your personal data sent outside of the UK/EEA? |
|---|---|---|---|
| SmartSearch | Identity Data, Contact Data, copies of identification documents, identity verification results and customer due diligence information. | To carry out electronic identity verification, sanctions screening, PEP screening, adverse media screening and customer due diligence. | No. |
- Financial providers who provide us with financial services and facilities;
| Third party | Personal data shared | Reason for sharing personal data | Is your personal data sent outside of the UK/EEA? |
|---|---|---|---|
| Banking providers and payment service providers used by VHQ | Identity Data, Contact Data, Financial Data and Transaction Data. | To process payments, administer banking facilities and manage financial transactions relating to our services. | No, unless the provider processes personal data outside the UK/EEA. Where this occurs, appropriate safeguards will be implemented. |
- If there is a change of ownership or control of our business, such as a merger, restructure, sale of the business or its assets or we acquire a new business, your information may be shared with the parties involved in this change. We will anonymise the information where possible and any recipients will be bound by contractual terms to keep such information confidential.
- We require all third parties to respect the security of your personal data and to treat it in accordance with the law and the terms of the contract we have in place with them where they are our third-party service providers. We do not allow our third-party service providers to use your personal data for their own purposes and only permit them to process your personal data for specified purposes and in accordance with our instructions.
- Please contact us at [email protected] if you want further information on the specific mechanism used by us when transferring your personal data out of the UK and/or EEA or you would like more information about the third parties we share your personal data with.
How do we keep your personal data safe?
- We have appropriate security measures in place to prevent your personal data from being accidentally lost, used or accessed in an unauthorised way, altered or disclosed. In addition, we limit access to your personal data to those employees, agents, contractors and other third parties who have a business need to know. They will only process your personal data on our instructions, and they are subject to a duty of confidentiality.
- We also have in place procedures to deal with any suspected personal data breach and will notify you and any applicable regulator of a breach where we are legally required to do so.
How long will we keep your personal data for?
- We will only keep your personal data for as long as necessary for the purposes we collected it for, including for the purposes of satisfying any legal, accounting, or reporting requirements. To determine the appropriate retention period for personal data, we consider the amount, nature, and sensitivity of the personal data, the potential risk of harm from unauthorised use or disclosure of your personal data, the purposes for which we process your personal data and whether we can achieve those purposes through other means, and the applicable legal requirements.
- In some circumstances we may anonymise your personal data (so that it can no longer be associated with you) for research or statistical purposes, in which case we may use this information indefinitely without further notice to you.
- Details of retention periods are set out in the table below:
| Data type | Retention period |
|---|---|
| Customers | Customer records and Customer Due Diligence (CDD) records are retained for 6 years after the business relationship ends in accordance with the Money Laundering, Terrorist Financing and Transfer of Funds (Information on the Payer) Regulations 2017. Where a longer retention period is required by law, we will retain the information for as long as necessary to comply with our legal obligations. |
| Prospective Customers | Where an application is not completed and no identification documents have been submitted, personal data will be retained for 3 months from the date the application is abandoned or closed. Where an application is declined following Customer Due Diligence, personal data will be retained for 6 years to comply with our legal and regulatory obligations. |
| Suppliers | Supplier records will be retained for 6 years after the end of the business relationship, unless a longer retention period is required to comply with legal, regulatory or accounting obligations. |
| Website visitors | Please see our Cookie Notice for information about the retention periods applicable to cookies and similar technologies used on our website. |
Third-party links on our website
- Our website may include links to third-party websites, plug-ins and applications. Clicking on those links or enabling those connections may allow third parties to collect or share personal data about you. We do not control these third-party websites and are not responsible for their privacy statements. When you leave our website, we encourage you to read the privacy notice of every website you visit.
Complaints
- You have the right to make a complaint to us about the processing of your personal data or in relation to the exercise of any of your rights at any time by contacting us using the details below.
- You also have the right to complain to the ICO, who can be found via their website (www.ico.org.uk) or by telephone: 0303 123 1113.
- We have appointed HelloDPO Law Ltd (https://hellodpo.com) as our Data Protection Officer.
- If you have any questions about this notice, including any requests to exercise your legal rights, please contact us using the details set out below:
t: +44 (0)330 223 2605
e: [email protected]
a: Virtual Headquarters Limited, Leigh Court Business Centre, Abbots Leigh, Bristol, BS8 3RA, United Kingdom.
Cookies
- Please see our cookie notice for details of the cookies we use on our website.
End of notice
-
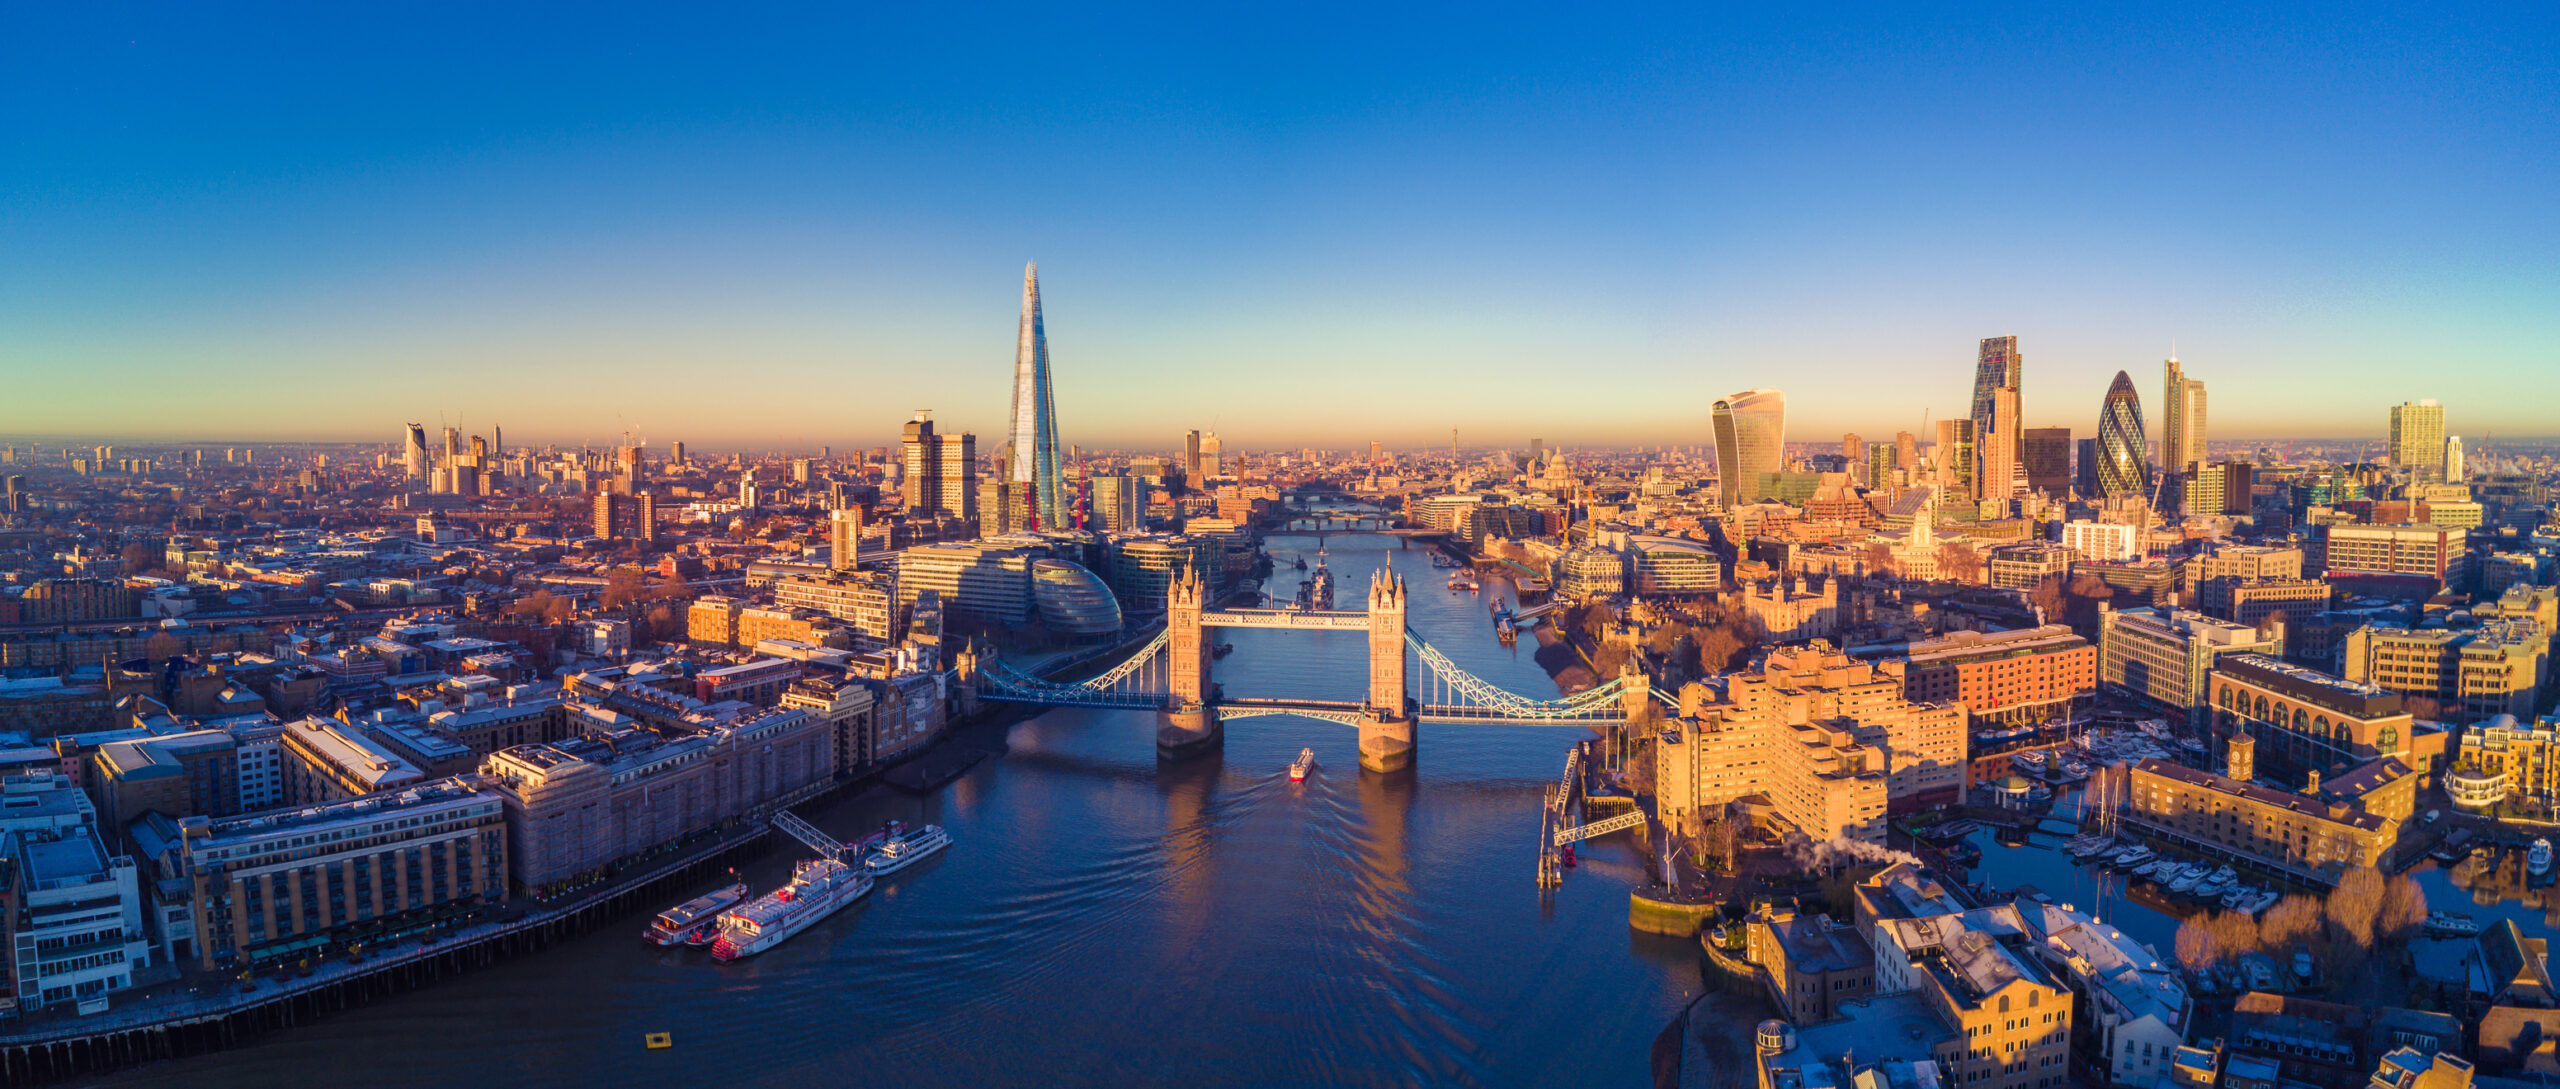
London
18 offices in London
-

Yorkshire
11 offices in Yorkshire
-
Somerset
11 offices in Somerset
-
Scotland
9 offices in Scotland
-
Greater Manchester
9 offices in Greater Manchester
-
Wales
7 offices in Wales
-
East Sussex
7 offices in East Sussex
-
West Midlands
7 offices in West Midlands
-
London City
6 offices in London City
-
Hampshire
6 offices in Hampshire
Can’t find what you’re looking for?
View all locations